Google Maps adds AI trip plans you can edit
U.S. users also get appointment-finding help, while Ask Maps expands into 30 European countries.
By Saeed Ezzati7 min read
The audio edition
Listen to this newsletter
0:005:19
Read transcript
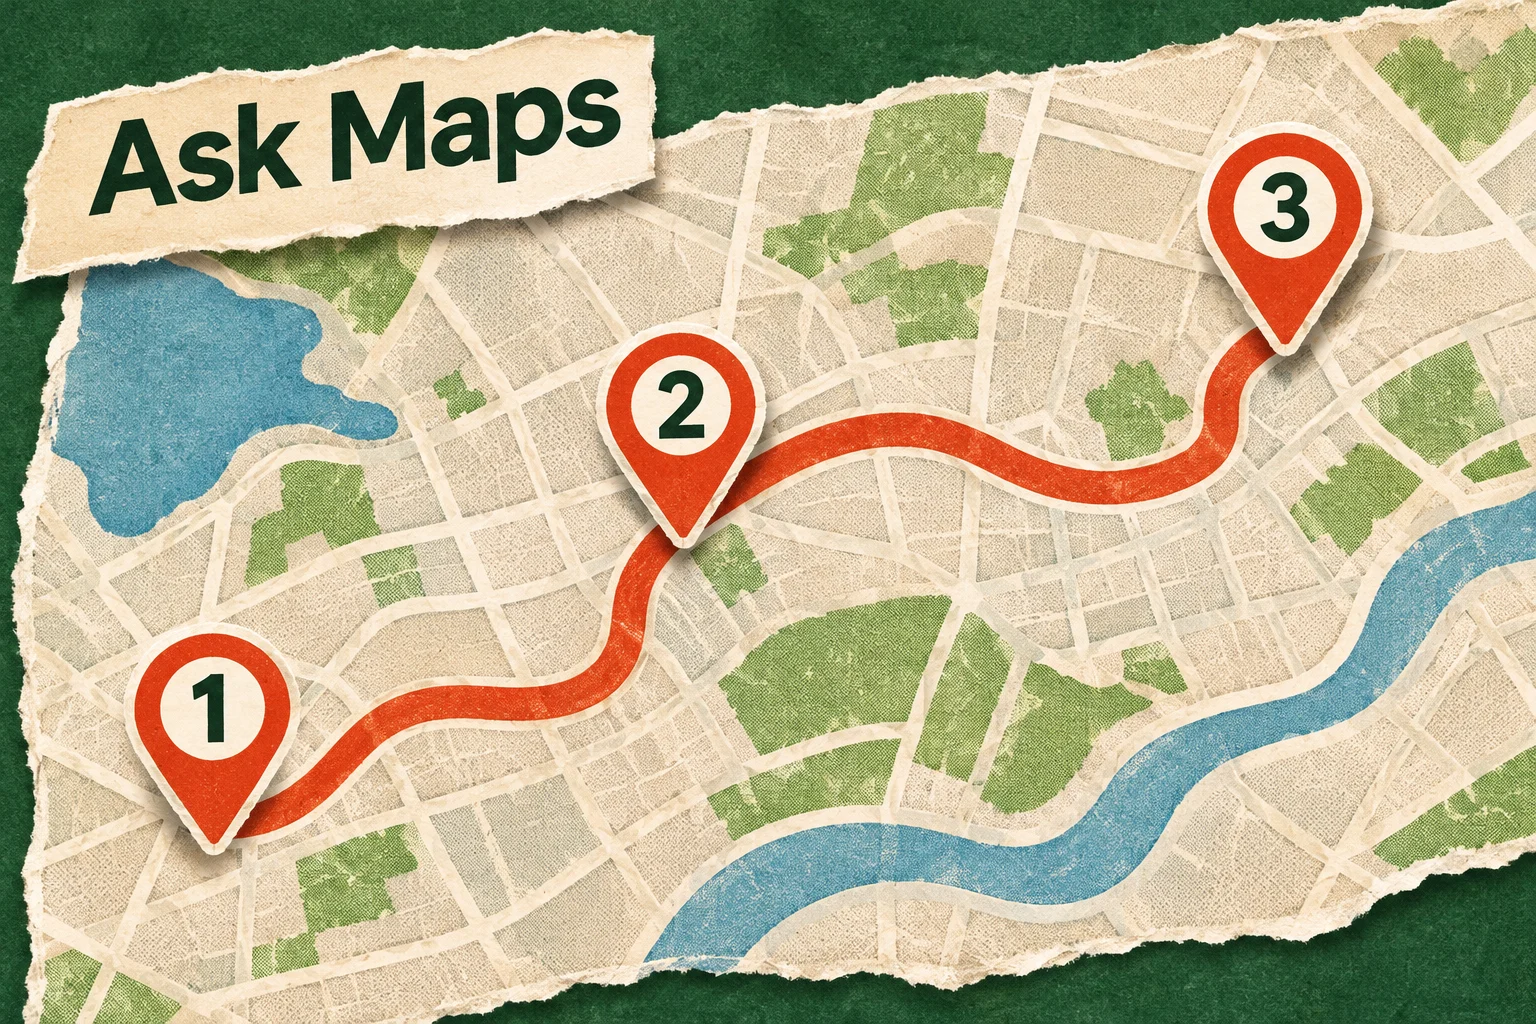
Google Maps is moving more trip planning into the map itself. Its Ask Maps assistant can now turn a request into an editable, map-linked itinerary, and check saved places for live availability. The rollout began November 16 on Android and iOS. Ask for a shopping day trip or a multi-day road trip, and Maps can lay out a schedule by day, with numbered pins showing each stop. You can ask it to add a scenic viewpoint or lunch, then tap through to directions. The plan can surface live traffic, opening hours and information about the next stop’s atmosphere. You can return to an itinerary through chat history, share it, or export it to Google Docs on desktop. There’s also a separate way to narrow down a saved list: ask which of your places can seat five people within the next 30 minutes, for example. Maps checks those saved venues against live availability, rather than making you scroll through them. Appointment search goes a step further. Google says Ask Maps can search online and call local businesses on a user’s behalf, then return available openings. Supported categories include beauty, pet care, auto repair and home repair. It finds slots; the user chooses what to book. The key caveat is geography. Itineraries and saved-place search are available wherever Ask Maps is offered. Appointment search and new route-preparation tips—covering parking, charging, weather, delays and tolls—start in the U.S. At the same time, Ask Maps is expanding into 30 European countries, taking its reach to more than 200 countries and territories. That expansion does not mean every feature is available everywhere. Google says the assistant combines Gemini models with information on more than 300 million places and reviews from more than 500 million contributors. The practical question is how well those connected details hold up when plans change on the day. That move from recommendations to doing the work is also showing up in healthcare, where OpenAI is offering computer-use agents through its API and healthcare products. They click and type across electronic health-record systems and insurer portals, including applications without useful software connections. The aim is to take on administrative handoffs: for example, gathering chart information for an MRI authorization and entering it into a separate insurer portal. In a demonstration, the agent drafted an order, note and patient reply for clinician review, then prepared an authorization request for a specialist to review. These are drafts and steps for people to check, not a claim that the agent independently makes clinical decisions. OpenAI says a CVS Health agent cleared a months-long document-sending backlog over a weekend. CVS uses validation checks and human oversight, including screenshots and action records. Organizations can also restrict actions, require approvals and inspect audit logs. HIPAA-compliant workflows still require eligible services, required settings and safeguards in connected systems. The operational test is not just whether an agent can cross a software gap, but whether its actions stay visible and reviewable. The same ability to act across disconnected systems creates a security concern: the FBI says multiple threat actors have used the AI-assisted ARTEX framework in attacks since at least August. The bureau warns that some intrusions reached elevated access in under three hours. ARTEX coordinates agents to investigate targets, exploit weaknesses and seek higher permissions, and can run operations against multiple organizations at once. The FBI says it can be conspicuous, generating enough automated traffic to trigger alerts, but still move too quickly for defenders to respond. Reported cases show how attackers can use trust already granted to cloud applications, or an old vendor credential that was never revoked. Those routes do not require breaking through every boundary from scratch. The FBI recommends reviewing application permissions and authentication logs, securing internet-facing systems and monitoring for bursts of automated requests and unexpected credential or permission changes. Its advisory includes technical indicators, but warns that some IP addresses may have changed. For operators, the useful check is whether old integrations still have access—and whether unusual activity would be noticed quickly. And in a less operationally consequential example of AI shaping a decision, Audible is adding spoken previews to help listeners choose audiobooks. The U.S. rollout covers select English-language titles and combines an AI-generated introduction, recorded commentary from an author or Audible editor, and a narrated excerpt. Audible says the generated overview draws on public reviews, book synopses and metadata, and describes themes and what readers liked. The commentary comes from past Audible interviews. So the format mixes generated narration with existing human recordings and a sample of the book itself; it is not an entirely synthetic preview. The selection of review material matters. The feature is described as emphasizing what readers liked, not as providing a balanced roundup of praise and criticism. TechCrunch notes that listeners could consequently hear less negative feedback, while cautioning that testing is needed to establish whether that happens. Across these stories, the useful thing to watch is what an AI feature can access, what it is allowed to do, and how its sources or actions can be checked. For Maps, that includes where each feature is available; for agents, permissions and approval trails; and for Audible, what kinds of reader response make it into the preview.