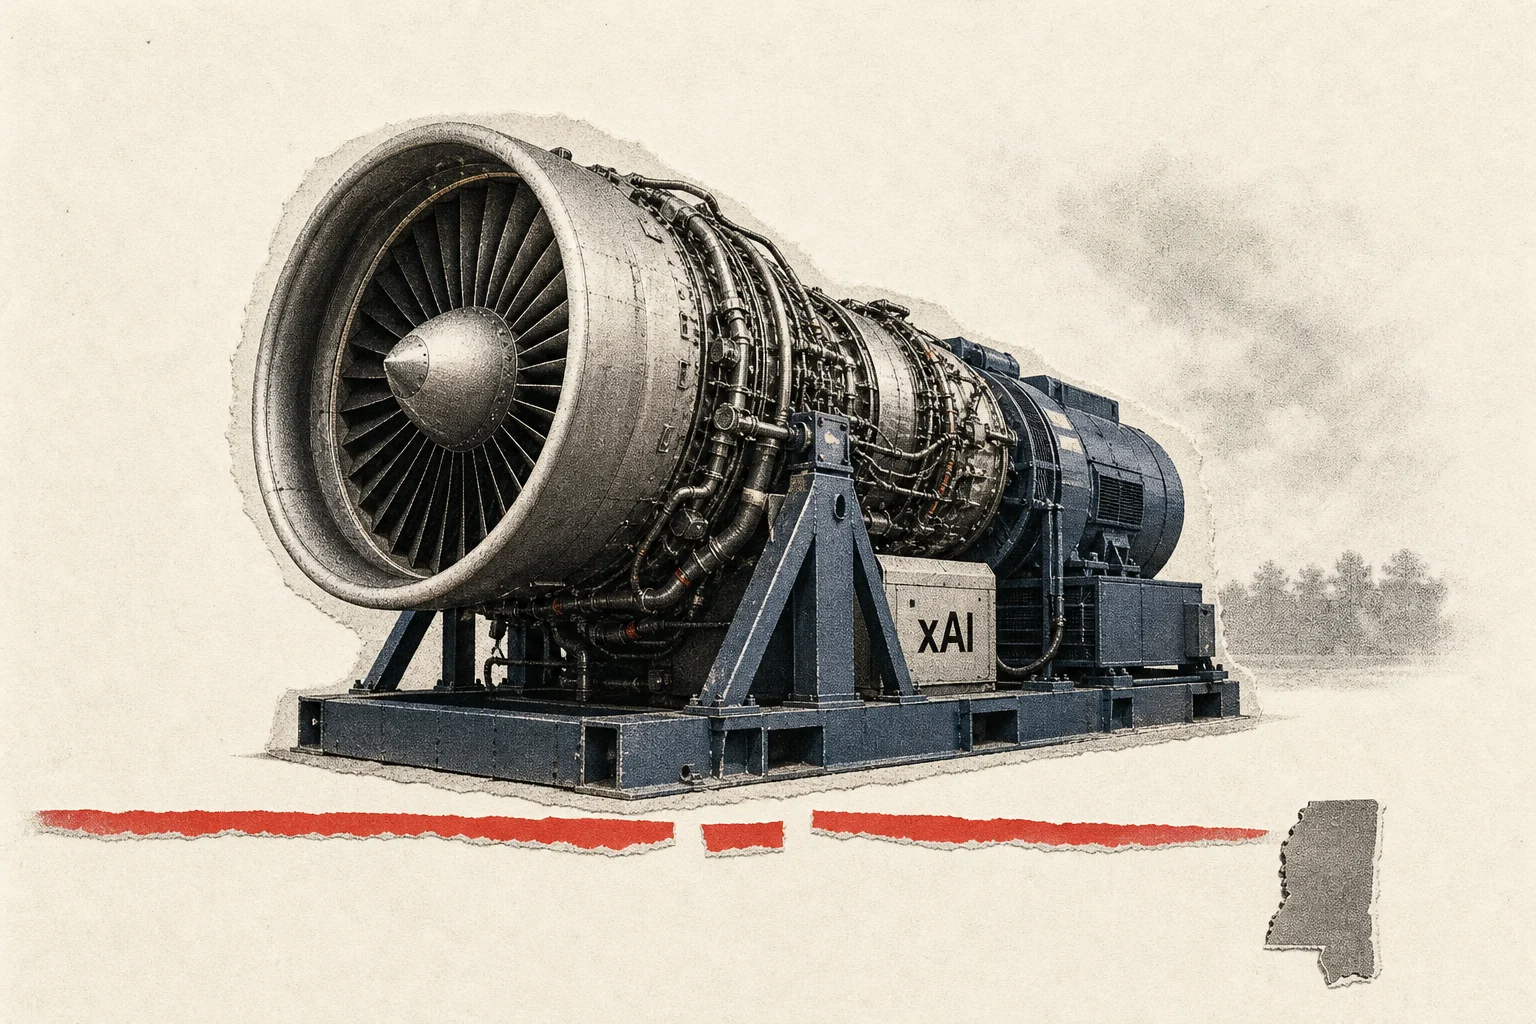
xAI powers a data center with eight jet engines
The Mississippi turbines have state permits, but an environmental group is challenging the emissions assurances.
By Saeed Ezzati8 min read
The audio edition
Listen to this newsletter
0:004:20
Read transcript
Eight converted jet-engine turbines are supplying electricity to an xAI data center in Mississippi, offering a way around power that traditional utilities have struggled to provide. The equipment comes from Missouri-based ProEnergy, which repurposes unused General Electric aircraft turbines as generators. Each turbine is rated for up to 50 megawatts. That’s its generating capacity, not a confirmed measure of what the Mississippi site is producing. The installation has state permits, but the Southern Environmental Law Center is challenging Mississippi’s approval over the emissions assurances and pollution estimates behind it. The center alleges xAI has not guaranteed compliance with limits for specific pollutants, including formaldehyde, and has undercounted projected emissions. It also raises concerns about carbon monoxide and volatile organic compounds. Those are allegations, not findings that the turbines have violated emissions limits. The distinction from an earlier dispute matters: that lawsuit alleged xAI used gas generators without required permits. This challenge is about approval already granted for these eight turbines—and whether the emissions estimates and assurances supporting that approval are adequate. So the tradeoff is concrete: a source of power outside constrained utility supply, with an unresolved fight over what the site may emit. The useful question is not simply how much power the turbines could generate, but whether their real-world operation matches the assumptions officials approved. On the production side of that same power-and-capability story, OpenAI says two employees used GPT-6 Astra to design a device for speaking to Codex in under a week. The work covered the enclosure, circuit board, interface and software—not just a concept image. But getting from design to a manufactured prototype took more work. A contract manufacturer made a small batch in under a month, after human reviews and several rounds of revision. Astra missed production tolerances and assembly details, so the model’s design still needed people to make it buildable. OpenAI also reported a higher score for a newer internal model on BenchCAD 2.0: 0.875, compared with 0.594 for Astra at its highest reasoning setting. That benchmark tests design tasks such as modeling parts and reconstructing circuit connections; it does not test manufacturability or physical performance. A strong design score, in other words, is not yet proof a factory can build the thing as intended. And the limits aren’t only technical: they include permission. Fanfiction site ao3.life shut down on November 2 after its creator said more than 2,000 takedown requests arrived in one day. The site had copied Archive of Our Own stories and sold AI-narrated audiobooks without the authors’ consent. It promised authors 91 percent of audiobook profits, but that offer did not mean they had agreed to have their work copied or sold. Its removal process also asked writers to prove ownership through their AO3 profiles, even though AO3 was offline during a security incident. The Organization for Transformative Works, which owns AO3, said the outage caused no data loss. That made the site’s preservation pitch especially fraught: access was interrupted, but the archive had not been lost. And when access is stolen rather than granted, the result can be an AI bill with no authorized deployment behind it. Google and Mandiant describe attackers pooling compromised cloud and model credentials, then reselling access through services that route customers’ requests to AI models. In one case, Google says a service using stolen API keys made more than 500,000 model calls in less than eight hours, leaving the victim with nearly a million dollars in token costs. That figure describes the victim’s bill, not verified access to every model the service advertised. Attackers also tested some stolen keys with requests limited to a single output token, potentially keeping those checks below volume-based alerts. In other incidents, they switched on AI services without permission. Google recommends treating unauthorized service activation as a serious security event, investigating suspicious low-volume requests, and setting spending limits. Across these stories, the shared operational test is whether capability is matched by control: verify the power and emissions assumptions, the design’s readiness for production, the rights to the data, and the credentials and spending behind AI use.